Kai Neumann · 6 September 2026
Analyzing Secure Annotation Systems for Professional Digital Workflows
Secure annotation systems integrate encryption, access controls, and audit logging into digital workflows that professionals use across legal, medical, engineering, and research sectors, and these platforms enable teams to mark up documents, images, and datasets without exposing sensitive content to unauthorized parties. Organizations implement such systems because regulations require data protection during collaborative review processes, while the technology supports version tracking that records every edit, comment, and highlight added by users.
Core Features That Define These Platforms
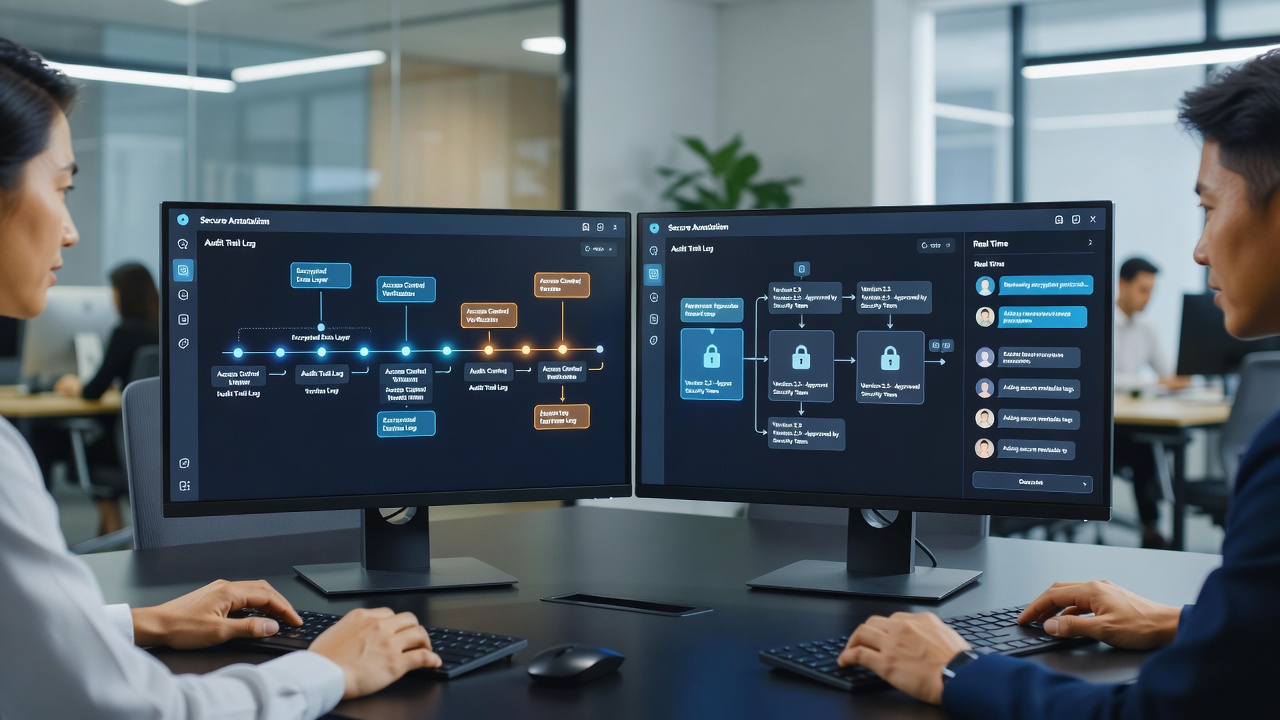
Encryption protocols form the foundation of secure annotation tools, and end-to-end methods ensure annotations remain unreadable during transmission and storage even if networks face interception attempts. Role-based permissions further restrict who can view or modify specific sections, whereas audit trails capture timestamps, user identities, and changes made so compliance officers can reconstruct any sequence of events later. Researchers at institutions studying digital security note that these combined elements reduce risks associated with shared files, and integration with existing enterprise software allows seamless adoption without disrupting established processes.
Multi-factor authentication adds another layer, and many systems now support single sign-on connections to corporate directories. Data segmentation techniques keep annotations separate from original files in some implementations, which helps when organizations need to share redacted versions with external partners.
Applications Across Professional Sectors
Legal teams rely on secure annotation for contract reviews where multiple attorneys highlight clauses and add notes that only authorized colleagues can access. Medical professionals use similar tools to annotate patient imaging and records while meeting privacy standards set by health authorities. Engineers annotate technical drawings during design iterations, and the systems maintain traceability that proves essential during audits or liability assessments.
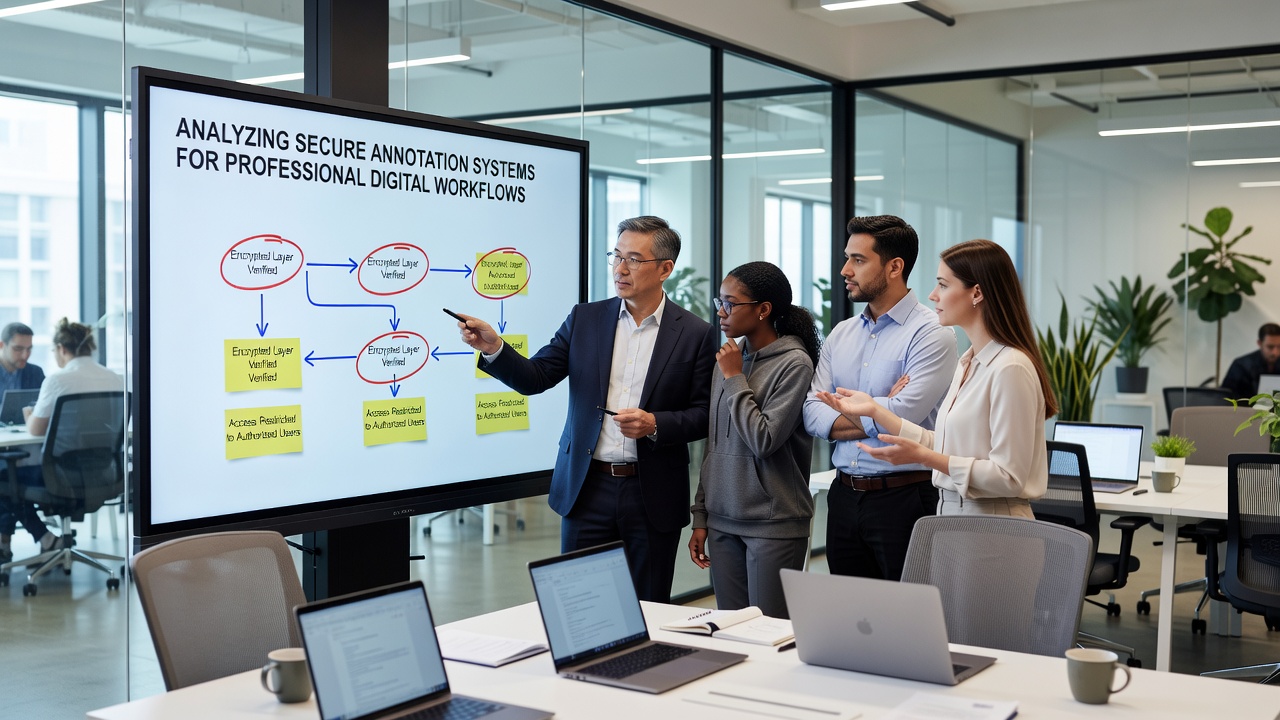
Academic researchers apply these platforms when collaborating on sensitive datasets, and annotations help track hypotheses or data interpretations without risking premature disclosure. Government agencies have adopted comparable solutions for classified document reviews, according to reports from cybersecurity agencies in multiple regions including the United States and Australia.
Security Standards and Compliance Requirements
Standards organizations publish guidelines that influence how vendors design annotation features, and compliance with frameworks such as those from the National Institute of Standards and Technology helps organizations demonstrate adherence during evaluations. NIST publications on data protection outline recommended controls that many secure annotation products incorporate. European agencies like ENISA provide additional guidance tailored to cross-border data flows, and companies operating internationally often align with both sets of recommendations to avoid conflicts.
What's interesting is how these requirements evolve, and updates scheduled for September 2026 aim to address emerging threats related to AI-assisted annotation and automated markup tools. Organizations preparing now review their current systems against draft specifications to identify gaps in logging or encryption strength.
Challenges in Implementation and Maintenance
Integration complexity arises when legacy software lacks modern APIs, and IT teams must develop custom connectors that preserve security properties throughout the workflow. User training represents another hurdle because staff accustomed to basic markup tools need instruction on permission settings and secure sharing procedures. Performance overhead from encryption can slow large file handling, although hardware acceleration and optimized algorithms mitigate this issue in newer releases.
Studies from university research groups indicate that regular security assessments help identify vulnerabilities before they affect operations, and penetration testing combined with code reviews forms standard practice among providers serving professional clients.
Conclusion
Secure annotation systems continue to advance as professional workflows demand both collaboration and protection, and ongoing developments in encryption and access management support these needs. Projections for September 2026 point to refined standards that will shape next-generation features, while organizations that align early with updated guidelines position themselves for smoother compliance. Data from industry reports shows continued adoption across sectors that handle confidential information, and the technical foundations established today provide the basis for future enhancements in audit capabilities and integration options.